A Scam Never Stays on One Channel.
7 min read
A representative cross-channel scam follows a consistent operational structure: initial contact through a text message impersonating a financial institution, escalation to a live phone call from an operator posing as a bank representative, redirection to a fraudulent payment interface replicating the institution's actual site, and a funds transfer executed through a digital wallet with no prior association to the victim's account.
Four distinct organizations are typically involved in this sequence: the telecommunications carrier that delivers the initial message, the voice network that carries the call, the platform hosting the fraudulent payment page, and the financial institution that processes the transfer. Each observes only a single, isolated segment of the interaction. None observes the coordinated operation as a whole.
One continuous scam
- Text MessageTelecom carrier sees this
- Phone CallPhone network sees this
- Fake Payment PageWeb platform sees this
- Bank TransferBank sees this
Four separate views. No shared picture.
The scale of the underlying problem is substantial. Identity fraud losses in the United States reached approximately $27 billion in 2024, an increase of roughly 19 percent over the prior year, with account takeover, the compromise of an existing account rather than the creation of a new one, accounting for more than half of that total. This trend has continued across multiple consecutive years, coinciding with sustained investment in fraud detection technology at the institutional level.
| Year | Account Takeover Fraud | All Identity Fraud |
|---|---|---|
| 2022 | $11.0B | $20.3B |
| 2023 | $12.7B | $22.8B |
| 2024 | $15.6B | $27.2B |
- Account takeover
- All identity fraud
This pattern illustrates the central limitation in current fraud detection architecture: the tools in use are not deficient, but a coordinated scam operation rarely remains within the single channel any individual detection system monitors, while the corresponding response almost always does.
Operational infrastructure is typically reused across multiple victims rather than rebuilt for each one, which is precisely what allows this gap to persist undetected. The same phone number recurs across several campaigns. The same script is used against different targets with only the impersonated institution's name substituted. The same fraudulent website remains active until independently reported, and the same destination account continues to receive transfers from victims with no connection to one another. Evaluated individually, none of these observations appears significant. Evaluated in aggregate, the pattern is unambiguous.
What Traditional Fraud Detection Actually Misses
Most fraud detection systems remain organized around single-event response rather than cross-event correlation. A suspicious payment triggers a review. A reported phone number is blocked after sufficient complaints accumulate. A fraudulent website is taken down once flagged. Each of these actions addresses a single symptom without exposing the operation producing it, a limitation that is most consequential when the transaction itself appears entirely legitimate, because the customer was not compromised technically. They were persuaded.
In the representative sequence described above, each stage carries an identifiable warning signal: manufactured urgency in the phone call, fear-based framing in the text message, a counterfeit representation of a trusted brand on the payment page, and a destination account with a documented history of receiving funds from unrelated victims. Each of these signals exists on a different organization's system, and none of those systems is built to evaluate signals originating elsewhere.
Connected Signals Outperform Isolated Detection
This is the same discipline cybersecurity teams have applied to threat detection for years: rather than evaluating each alert as an isolated, unprecedented event, indicators are correlated against known patterns and evaluated in terms of their relationships to one another. The same discipline applies directly to Scam detection: a phone number correlated to the email address it routes to, that email correlated to the website it directs toward, and that website correlated to the payment account ultimately requesting funds.
Signal-based detection
Connected intelligence
The distinction between the two approaches is significant. Signal-based detection evaluates one alert at a time against a known indicator set, and its effectiveness depends on the persistence of those indicators; substituting a new phone number or registering a new domain is sufficient to defeat it. Connected intelligence is comparatively indifferent to any single identifier. It evaluates relationships between signals, which allows detection to remain effective even after every individual identifier has been changed.
One approach blocks a number. The other exposes the campaign the number belonged to.
Identity verification and connected intelligence address different questions. Identity verification confirms that a claimed identity is plausible at a specific point in time; it does not, and structurally cannot, evaluate the account's subsequent behavior. An operator impersonating a bank representative, a fraudulent investment platform replicating an established brand, or a cluster of accounts constructed from variations of the same stolen credentials can each satisfy identity verification requirements without difficulty, because verification is scoped to a single moment rather than an ongoing pattern. An account can pass verification and still accumulate multiple Scam reports, a pattern of suspicious communications, and payments traceable to other victims. Identity signals are most informative when evaluated alongside behavioral activity, not as a substitute for it.
Following the Scam Past the First Alert
The relevant question is not whether a single interaction appears suspicious, but where a Scam originated, what occurred immediately afterward, which accounts, numbers, and websites connect back to it, and whether the same pattern has appeared elsewhere previously. Most fraud detection systems were not designed to answer that category of question, and the difficulty of answering it increases with organizational size.
Most large organizations operate fraud detection, identity verification, payments, customer support, and reporting as separate systems, each managed by a different team with visibility limited to its own function. Scam operations are not constrained by those internal boundaries, and a single campaign can move through a telecommunications provider, a bank, a payment platform, and a customer support queue before any of them recognizes they are observing the same operation from different angles.
This condition is not limited to internal organizational boundaries. The organizations typically involved in a cross-channel Scam, telecommunications carriers, voice network operators, payment platforms, and banks, operate in different industries, under different regulatory frameworks, with no existing commercial relationship to one another. A telecommunications carrier has no established business reason to share signal data with a specific bank, and a bank has no standing channel through which to request it, because the two are not competitors, partners, or counterparties in any conventional sense. They are connected only incidentally, through having each been used by the same operation.
This is a materially different condition than reluctance to cooperate within a single industry. It is the absence of any existing relationship or mechanism through which cross-industry coordination could occur at all. No individual participant has the standing, the incentive, or the technical capacity to construct that connective layer unilaterally, which is the condition under which a dedicated, independent intelligence layer becomes structurally necessary rather than optional.
Context is what converts an isolated phone number into an informative signal. In isolation, a phone number conveys minimal information. Correlated with a script used against a dozen prior victims, a website replicating a bank's login page, and a set of payment accounts linked to one another, the same number becomes substantially more informative. The shift from a single flagged item to a mapped operation constitutes the core value of connected intelligence: the difference between identifying that something appears suspicious and establishing what it is actually part of.
None of this requires replacing the fraud detection tools organizations have already deployed. It requires connecting what those tools already observe. A Scam that moves from a text message to a phone call to a fraudulent website to a bank transfer does not constitute four unrelated events. It is a single operation presented through four different channels, and identifying it as such requires evaluating all four together.
Common Questions
What is connected fraud intelligence?
The practice of correlating signals across channels, phone numbers, messages, websites, identities, and transactions, to identify relationships that indicate a coordinated operation rather than a single isolated alert.
Why can't a bank detect this from the transaction alone?
Because the transaction itself frequently appears entirely legitimate. The customer was not technically compromised; they were persuaded, typically through a call or message that never interacted with the bank's own systems.
How is this different from standard fraud detection?
Standard detection evaluates individual events, a suspicious payment, a reported number, a flagged website, independently. Connected intelligence correlates those events, making a pattern that spans multiple channels visible rather than appearing as several unrelated incidents.
Does this replace identity verification?
No. Identity verification confirms who someone claims to be at a given moment. Connected intelligence addresses a separate question: what that same identity or account does afterward, across every channel it touches.
Where does Avert Intelligence fit into this?
Avert Intelligence aggregates Scam reports and evidence generated through Unscammed's reporting infrastructure into connected intelligence that banks and enterprises can act on before the next victim is contacted.
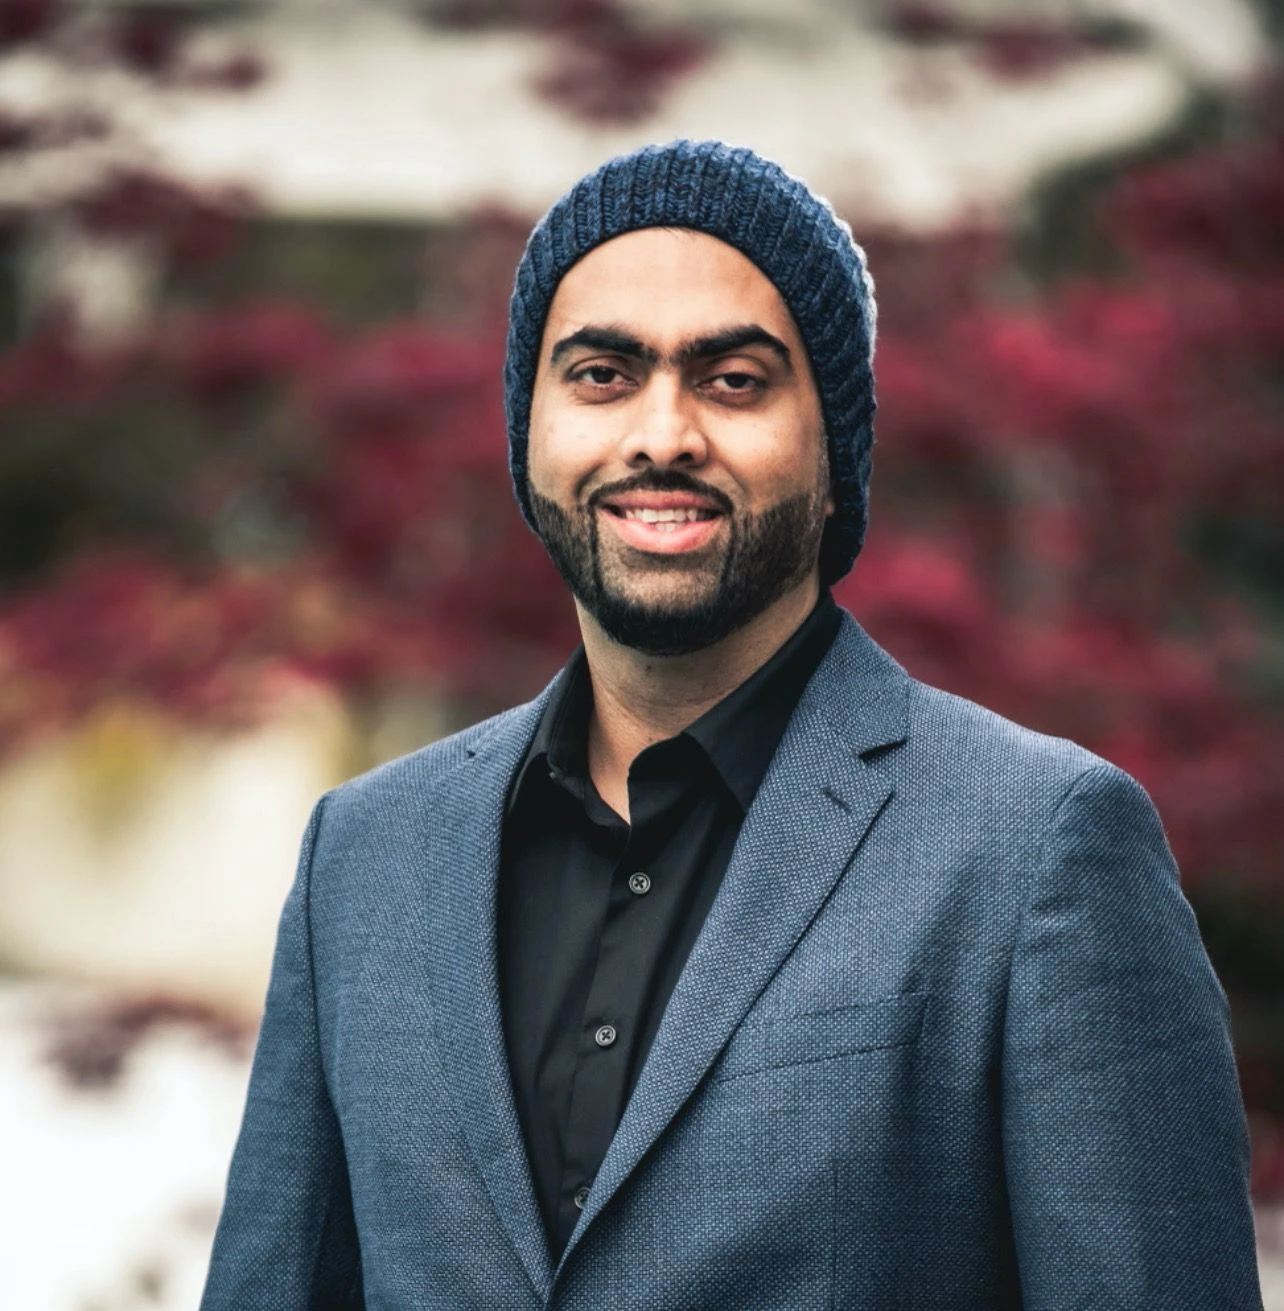
Sahil Pruthi — CEO
Sahil has spent a decade on the front lines of fraud and cybersecurity. Previously as Head of Product for Innovation at Norton Lifelock, he built Norton Genie - the world's first AI model to detect scams in calls, texts and emails, and scaled other product lines to over $60M in ARR. Now, he's channeling that experience into Avert Intelligence, driven by a single mission: a scam-free world, where every organization has the intelligence it needs to keep its customers safe before a scam ever reaches them.